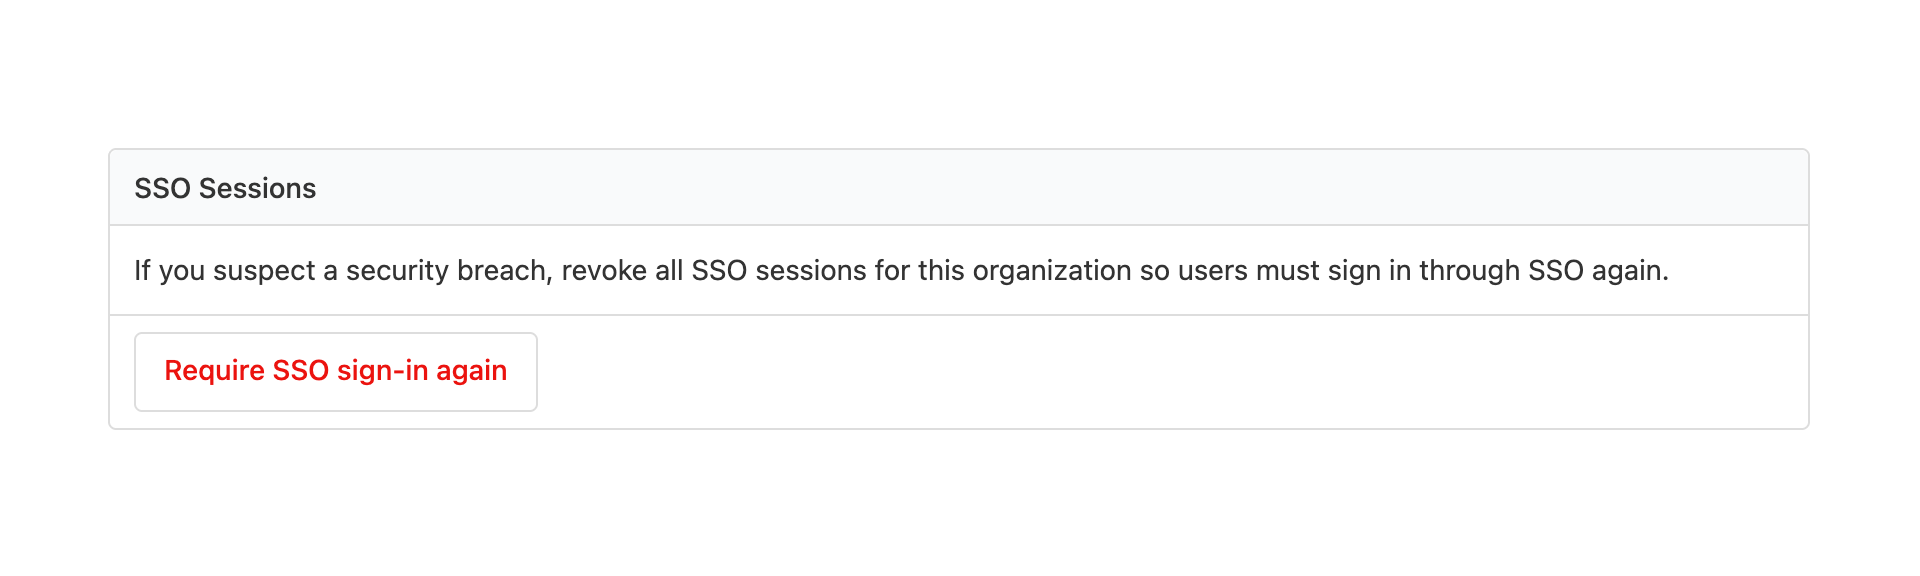
- Admins can now force all organization members to re-authenticate via SSO from Settings → Security → Require SSO sign-in again.
- Only SSO sessions are revoked; existing API, agent, and OAuth tokens remain valid and must be revoked separately.
- Members must sign in through the identity provider again; sessions for other orgs and SSO‑exempt members are unaffected.