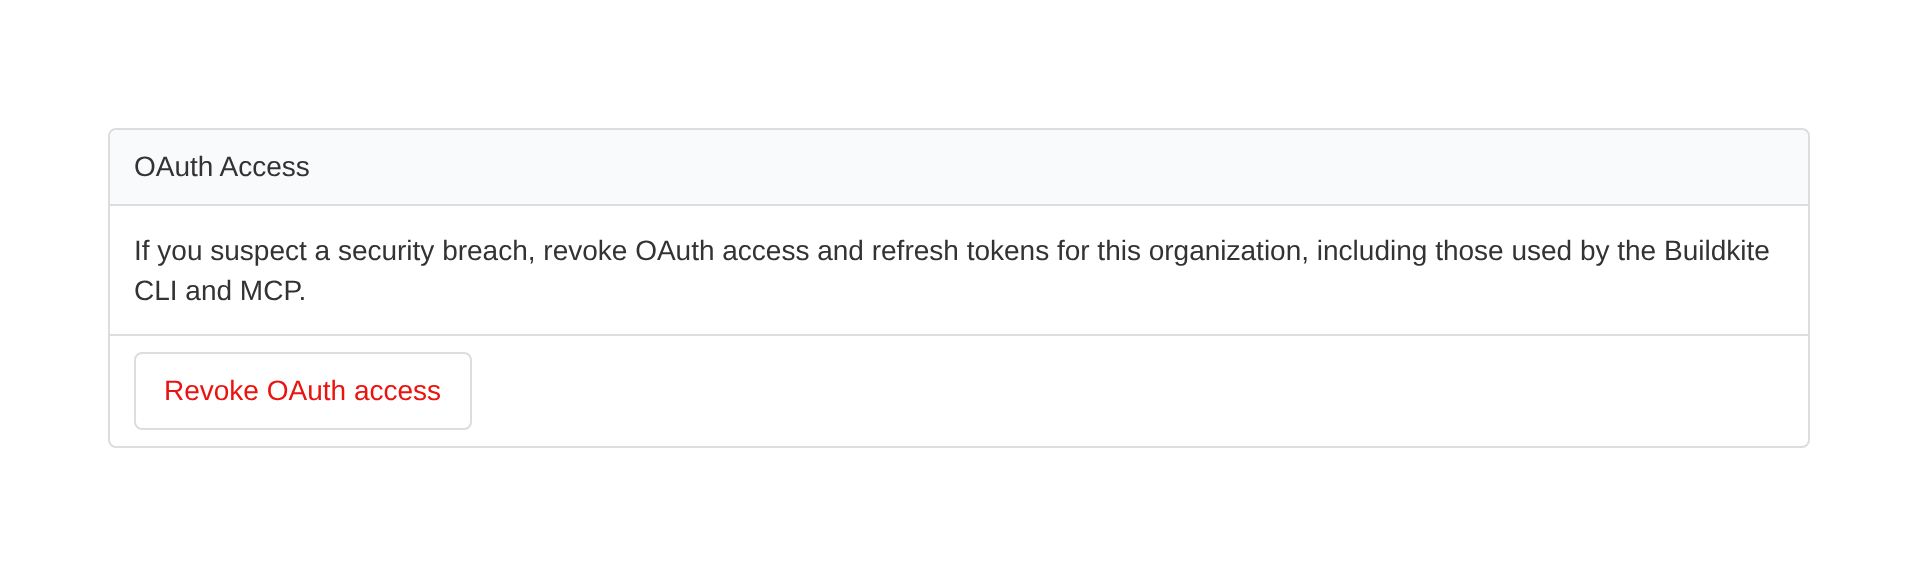
- Admins can now revoke all OAuth access and refresh tokens for their organization via Settings → Security → General.
- Revocation runs in the background, disabling existing OAuth integrations (including Buildkite CLI) until re‑authorized; other token types remain unaffected.
- New authorizations after revocation continue to work.